- The Louvre's security system relied on Windows Server 2003, closely linked to Windows XP, which has not been supported since 2015.
- Libération and i3e point to eight surveillance programs purchased in 2003, without maintenance; one from Thales operated without support from the parent company Sathi.
- Weak passwords such as "LOUVRE" and "THALES" would have facilitated access to and manipulation of video surveillance.
- ANSSI warned in 2023 of the need to migrate outdated systems; i3e describes a cluster of obsolescence and lack of security infrastructure.
An investigation has revealed that the Louvre Museum maintained its security system using legacy Windows XP systems, specifically machines running Windows Server 2003, a platform that has been unsupported for years. The combination of outdated software, old hardware, and weak security policies created an environment ripe for intrusion into this critical infrastructure.
Sources consulted by French media, as well as the technology group i3e, indicate that the Parisian museum's security system operated with software acquired in 2003 and without maintenance contracts, while access passwords were excessively simple. This context is related to the robbery that shocked France on October 19, which was carried out in a matter of minutes.
How the system was exposed
The core of the environment was Windows Server 2003 , an edition related to Windows XP whose official support ended in 2015, meaning there are no patches for known vulnerabilities . In high-crime scenarios, this gap significantly increases the exposure to attacks using tools available today.
Furthermore, the operation relied on eight surveillance applications purchased in 2003 , which lacked active maintenance from their suppliers. These included solutions from Thales, and 2019 tender documents indicated that one of these critical programs ran on Windows Server 2003 and was not supported by Sathi, the parent company.
This situation was compounded by inappropriate practices: basic passwords such as "LOUVRE" were used for the video surveillance server and "THALES" to access associated software, which paved the way for modifying credentials and manipulating cameras in a short time.
i3e emphasizes that this was not an isolated failure, but rather a combination of obsolescence and lack of controls , where old systems, unsupported applications, and hardware that no longer fulfilled its function in a secure environment coexisted.
Previous alerts and investigations in France
The National Agency for Information Systems Security (ANSSI) had already pointed out in 2023 the urgent need to migrate the museum's outdated systems, according to an internal report cited by the press. Despite these recommendations, the necessary changes were not implemented in time.
According to Libération and i3e's analysis, in addition to using Windows Server 2003—derived from the Windows XP technology base—the museum did not contact developers to update critical services, leaving an operational and cybersecurity gap.
Implications for Europe and the cultural sector
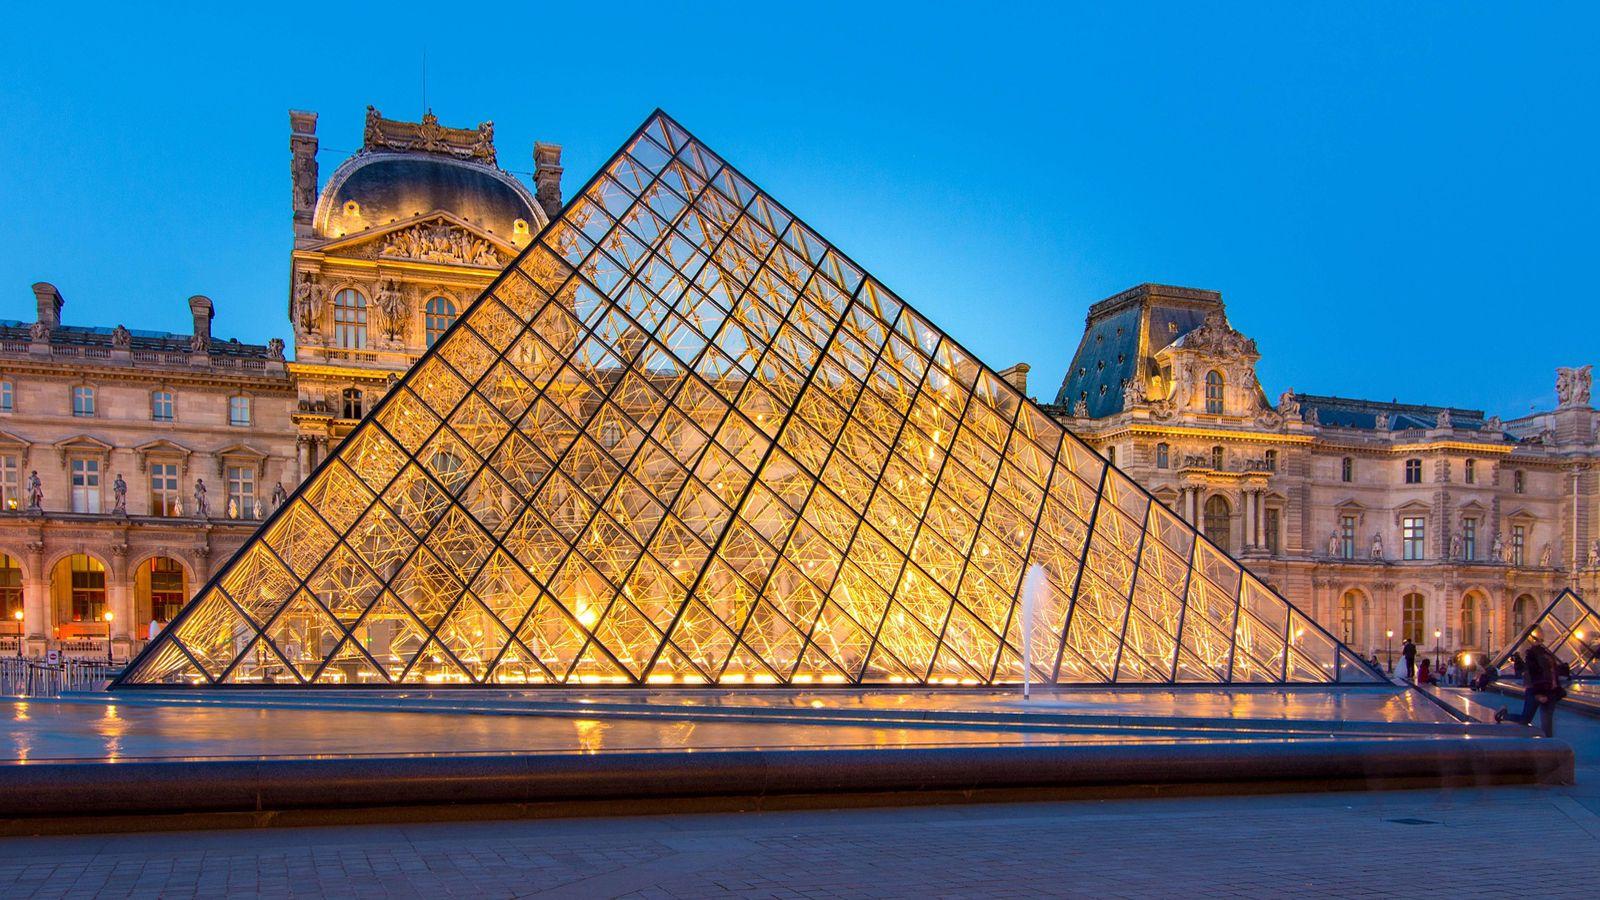
The Louvre case serves as a warning to European cultural institutions, including those in Spain, where heritage protection demands that cybersecurity be integrated into the physical perimeter . Unsupported systems, weak passwords, and a lack of maintenance are not merely IT problems: they jeopardize priceless collections.
In a context of growing threats and more demanding regulatory frameworks, the lesson is clear: it's not enough for equipment to simply keep turning on . It's essential to guarantee updates, network segmentation, and continuous monitoring so that security doesn't depend on outdated components.
What measures are being put on the table
Experts consulted insist on strengthening solid maintenance contracts and regular audits , vulnerability monitoring, and a technology renewal plan that progressively replaces old systems with supported versions.
They also recommend strong password policies and multi-factor authentication for critical access, inventory and asset control, as well as ongoing training for monitoring personnel to detect and correct vulnerabilities before they are exploited.
The most common consensus among experts is that it wasn't a single component that failed, but the entire system : unsupported software from 2003, an operating system tied to Windows XP that was no longer supported, and lax operational practices. From now on, European museums with similar infrastructures have a clear roadmap to increase their resilience without delay.